At Table Level
Table permissions in NocoDB control what users can see and what actions they can perform in a table. Visibility sets if a table exists for a user. Record permissions set who can create or delete records in that table. The download permission sets who can export its data.
Table Visibility
Table Visibility sets if a user can find and open a table and its views in a project. When a table is visible, the user can use it as their roles and permissions allow. When a table is not visible, NocoDB treats it as not there for that user.
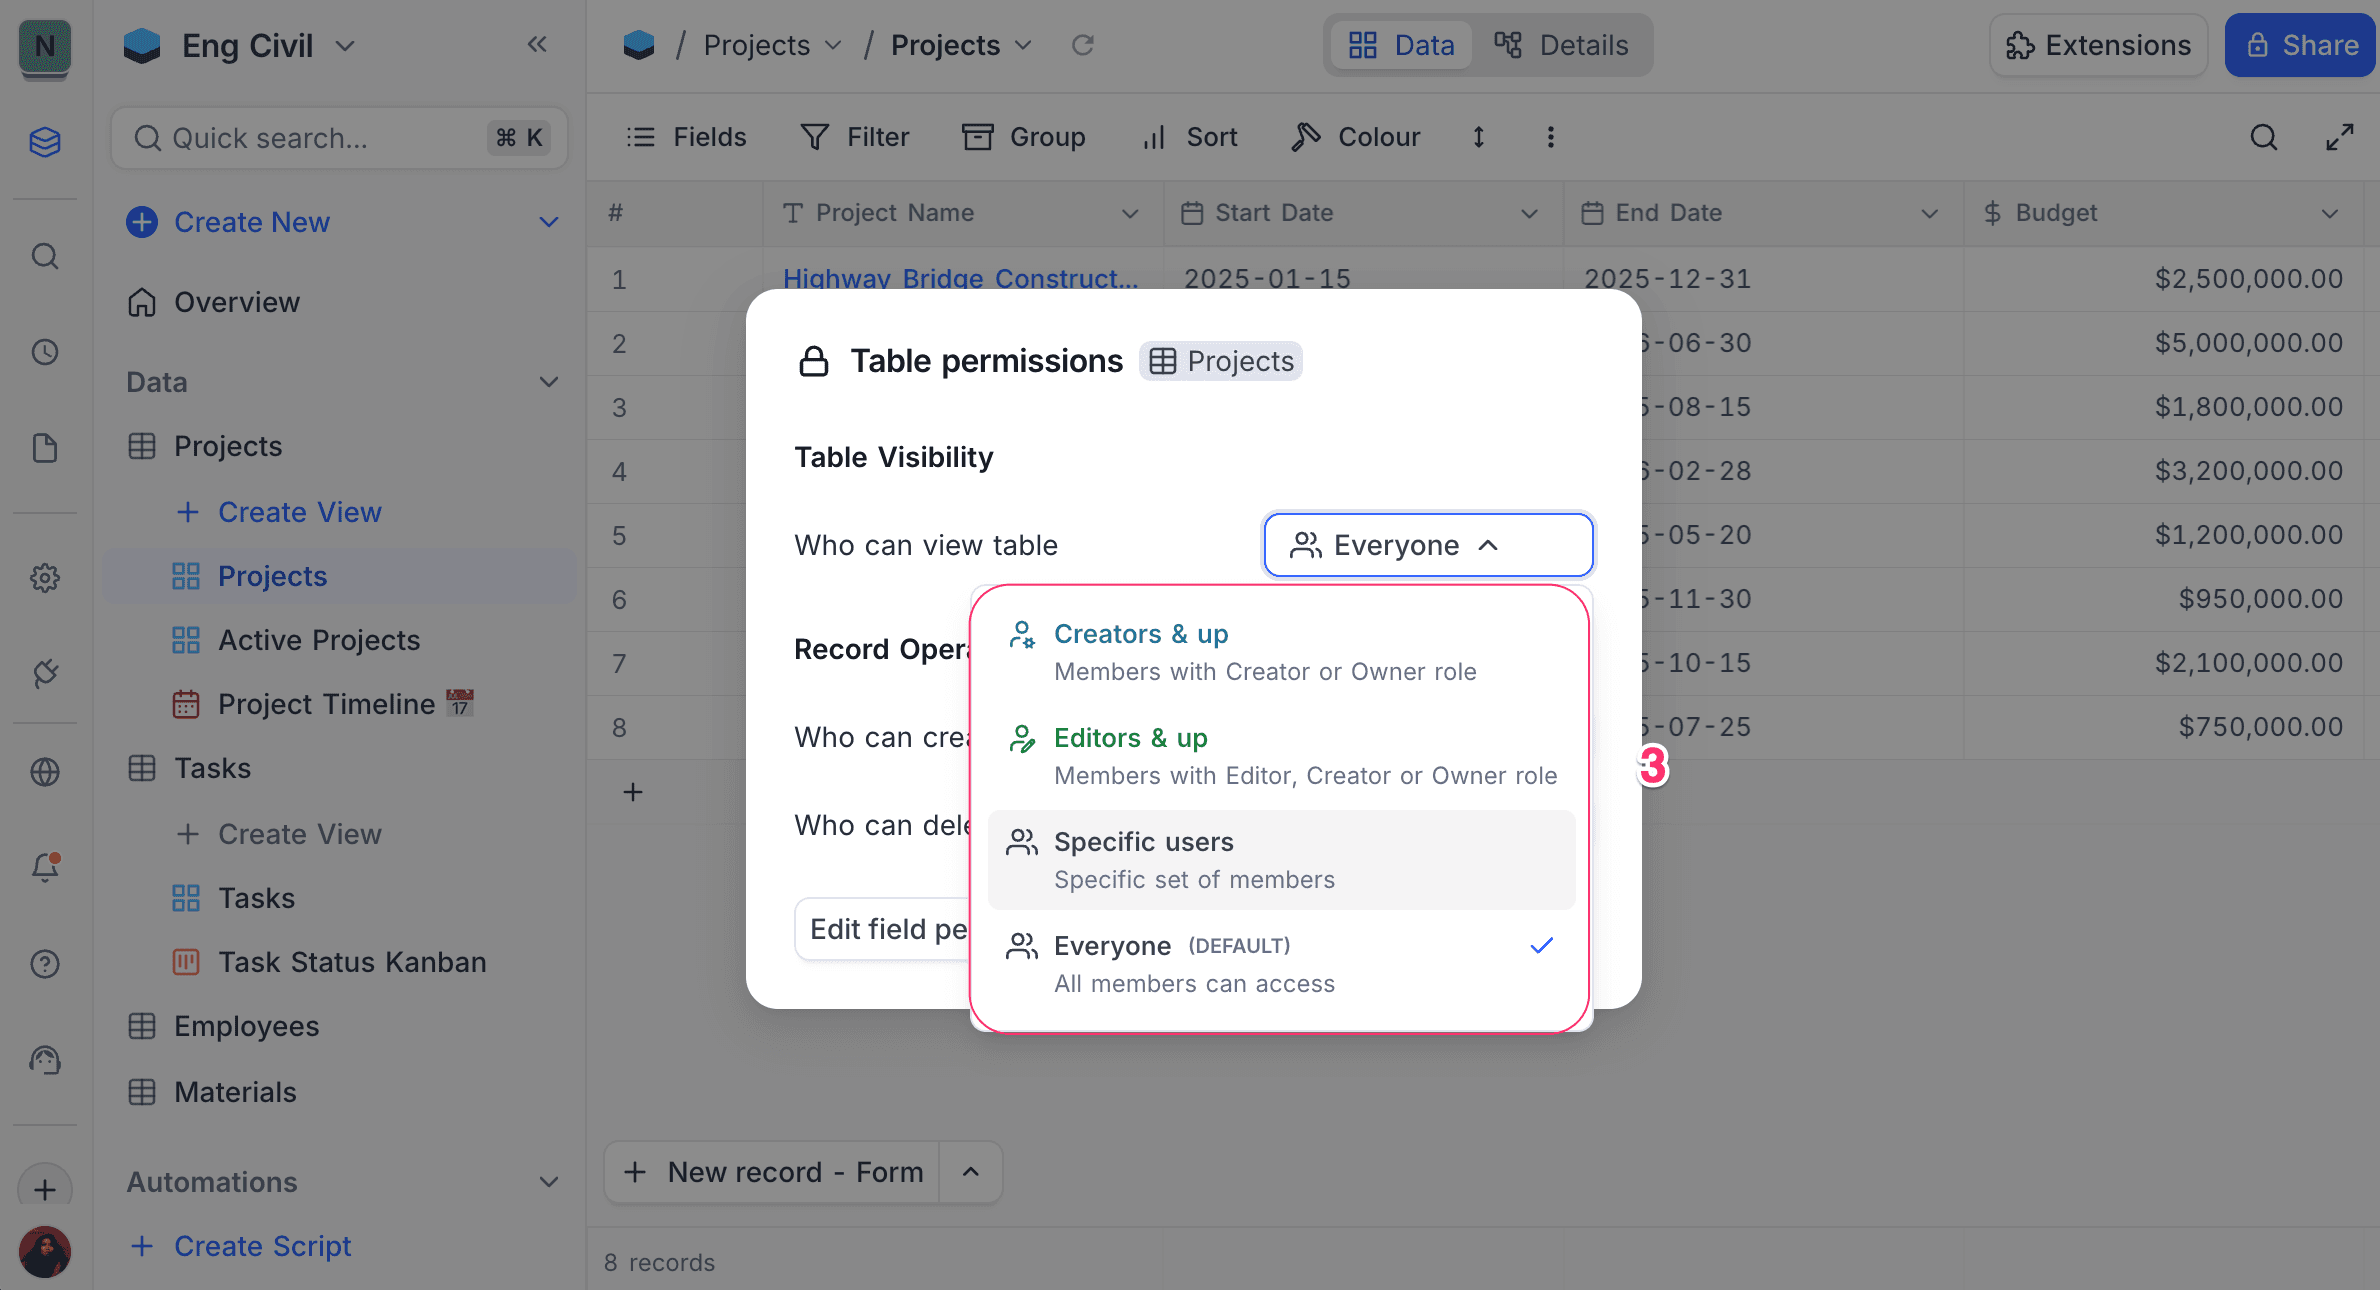
These are the visibility options:
| Option | Who can see the table |
|---|---|
| Creators & up | Members with Creator or Owner roles |
| Editors & up | Members with Editor, Creator, or Owner roles |
| Specific users | Only selected members or teams |
| Everyone | All members of the project (default) |
Note:
- By default, all tables are visible to everyone in the project.
- Table visibility is evaluated before checking record permissions. If a table is not visible to a user, they cannot access it or perform any actions within it, regardless of their record permissions.
- Hidden tables will be excluded from APIs, Automations, Scripts & Extensions that list or access tables.
Configuring Visibility
To configure the visibility of a specific table:
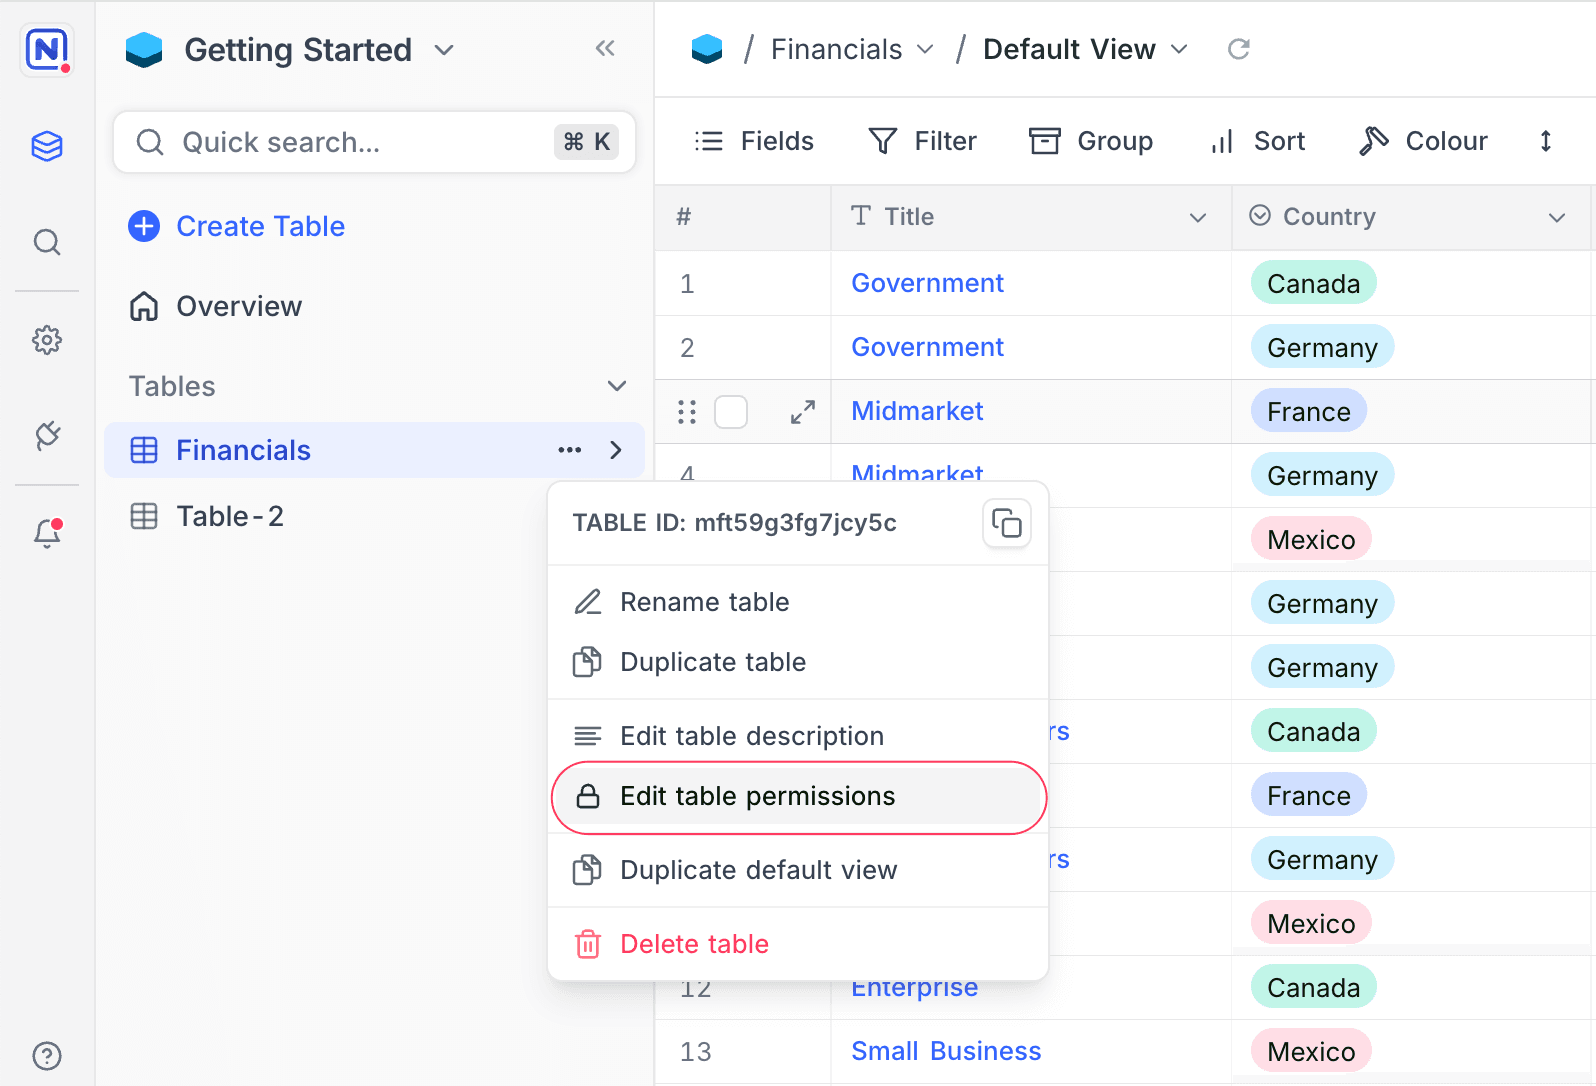
- In the sidebar, click the
⋯icon next to the table name. - Select Edit table permissions.
- Use the dropdown menu next to Who can see this table? to set the visibility.
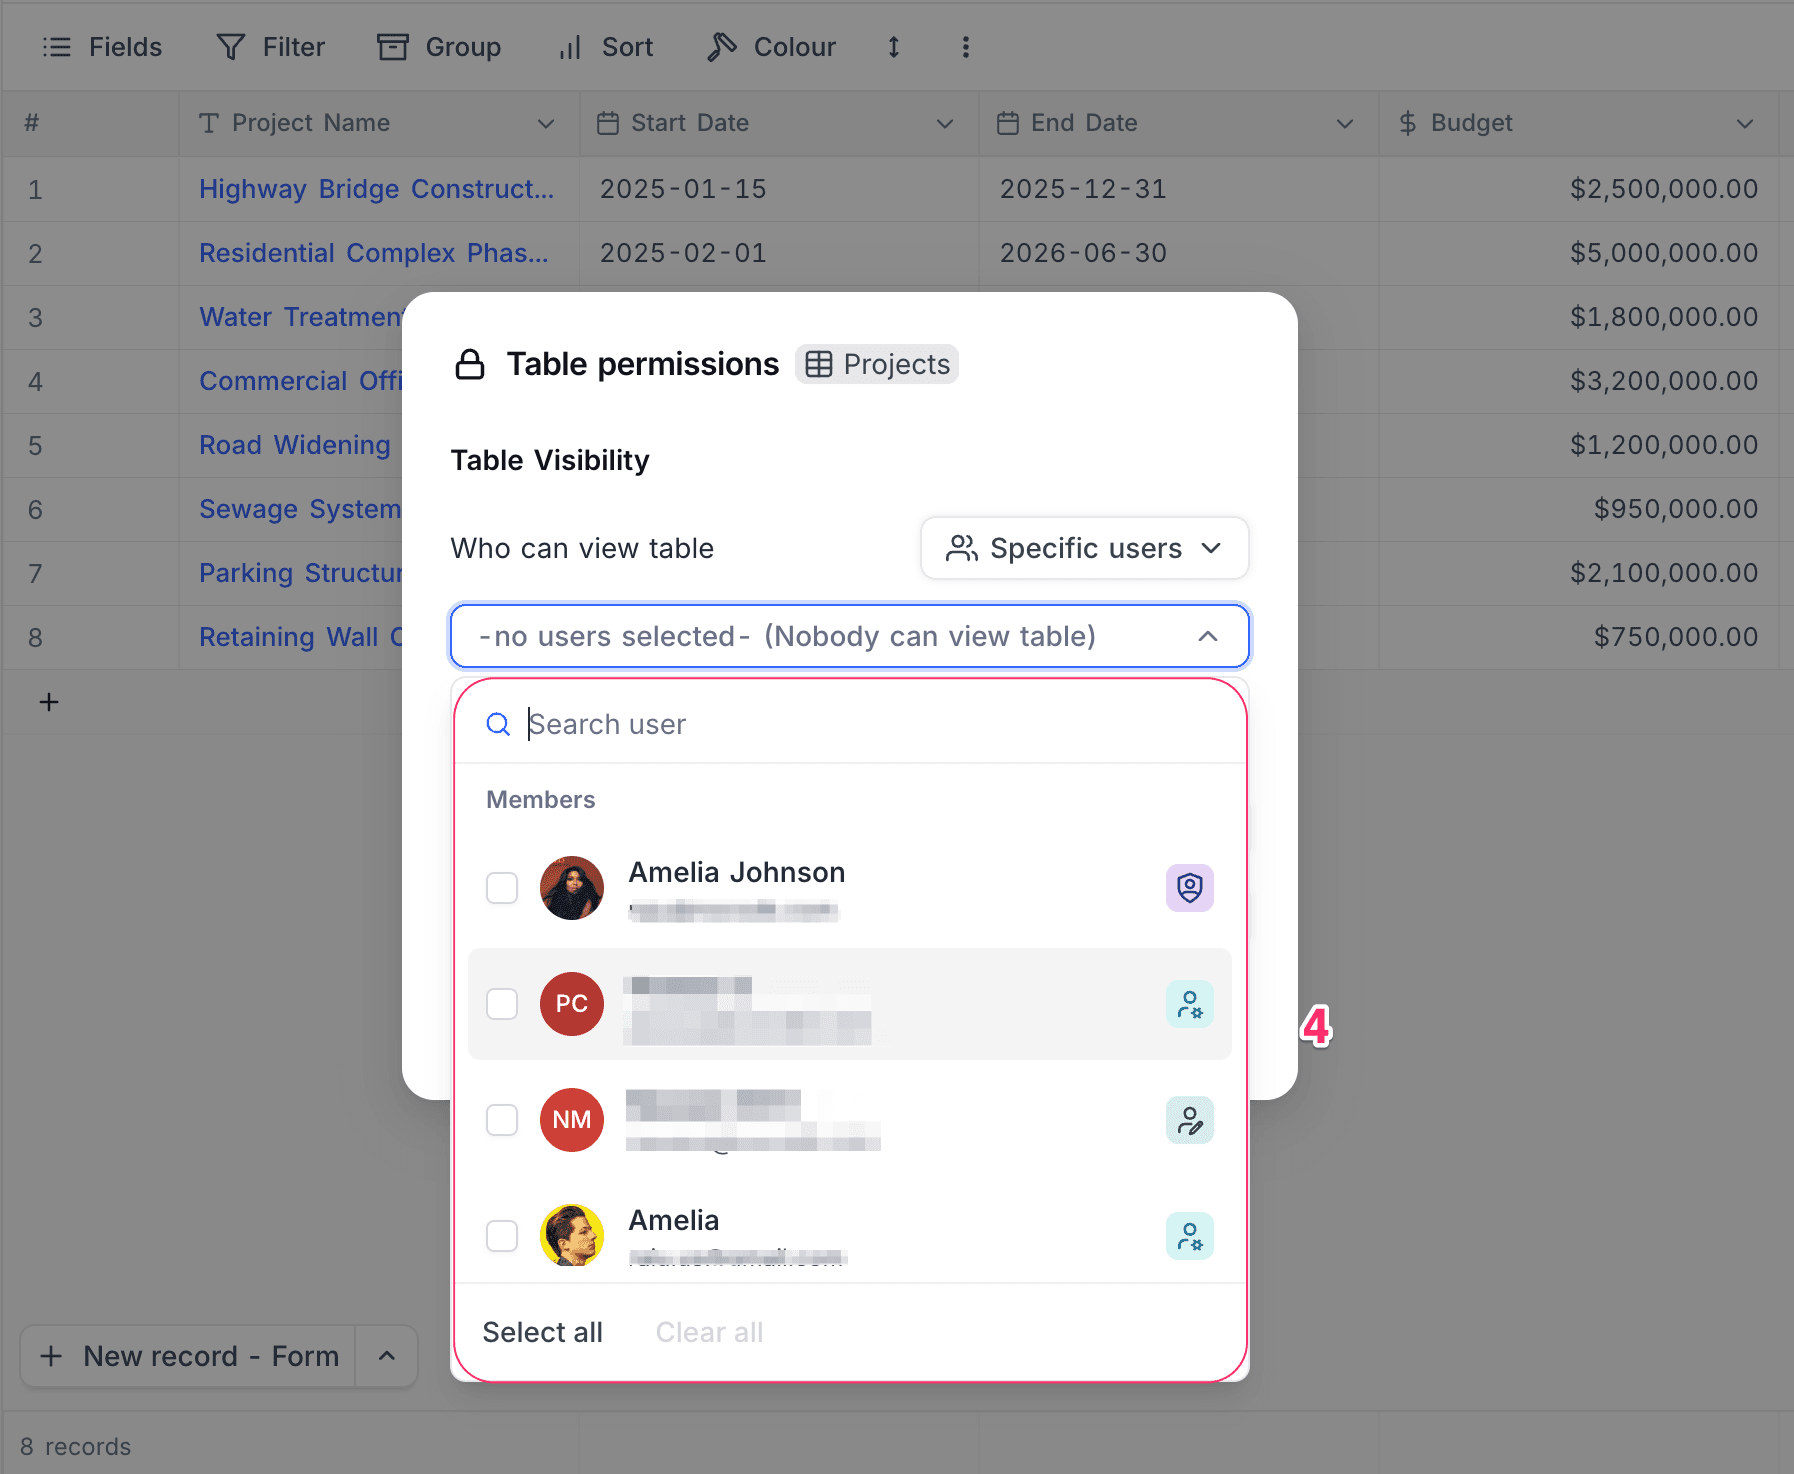
- If you select Specific users, select the members or teams that can access the table.
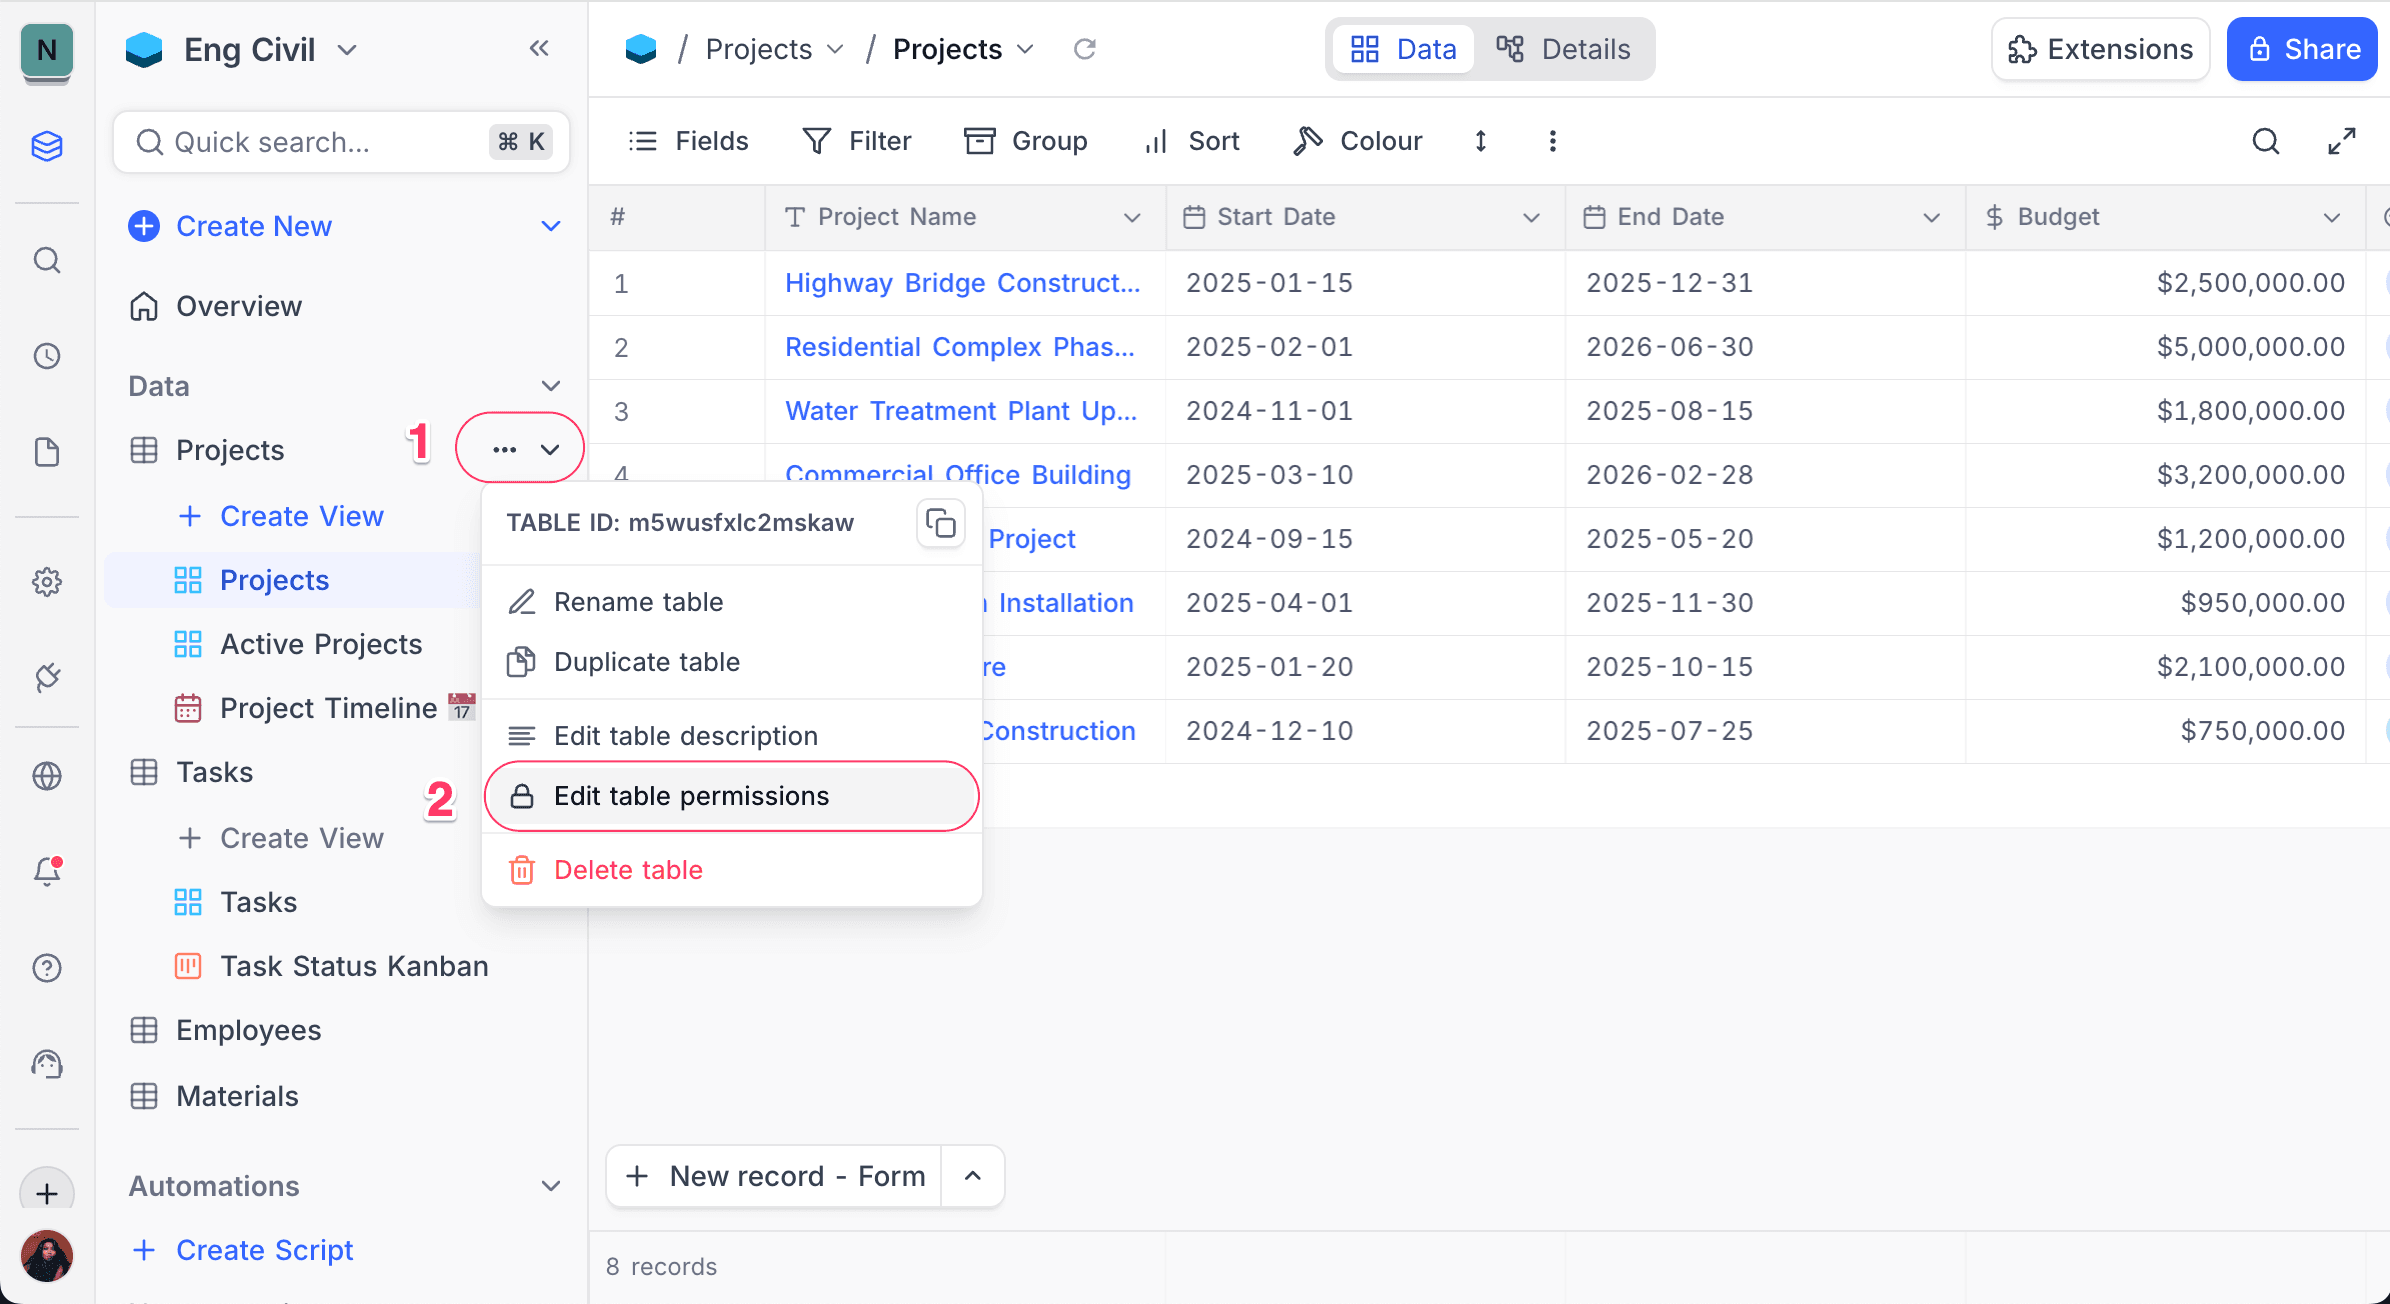
Only Project Owners can change table visibility settings. Other members do not see this option in the menu.
Visibility Notes
Shared projects and shared views Table visibility applies to shared access. In a shared project or shared view, you can access only the tables with the visibility option Everyone.
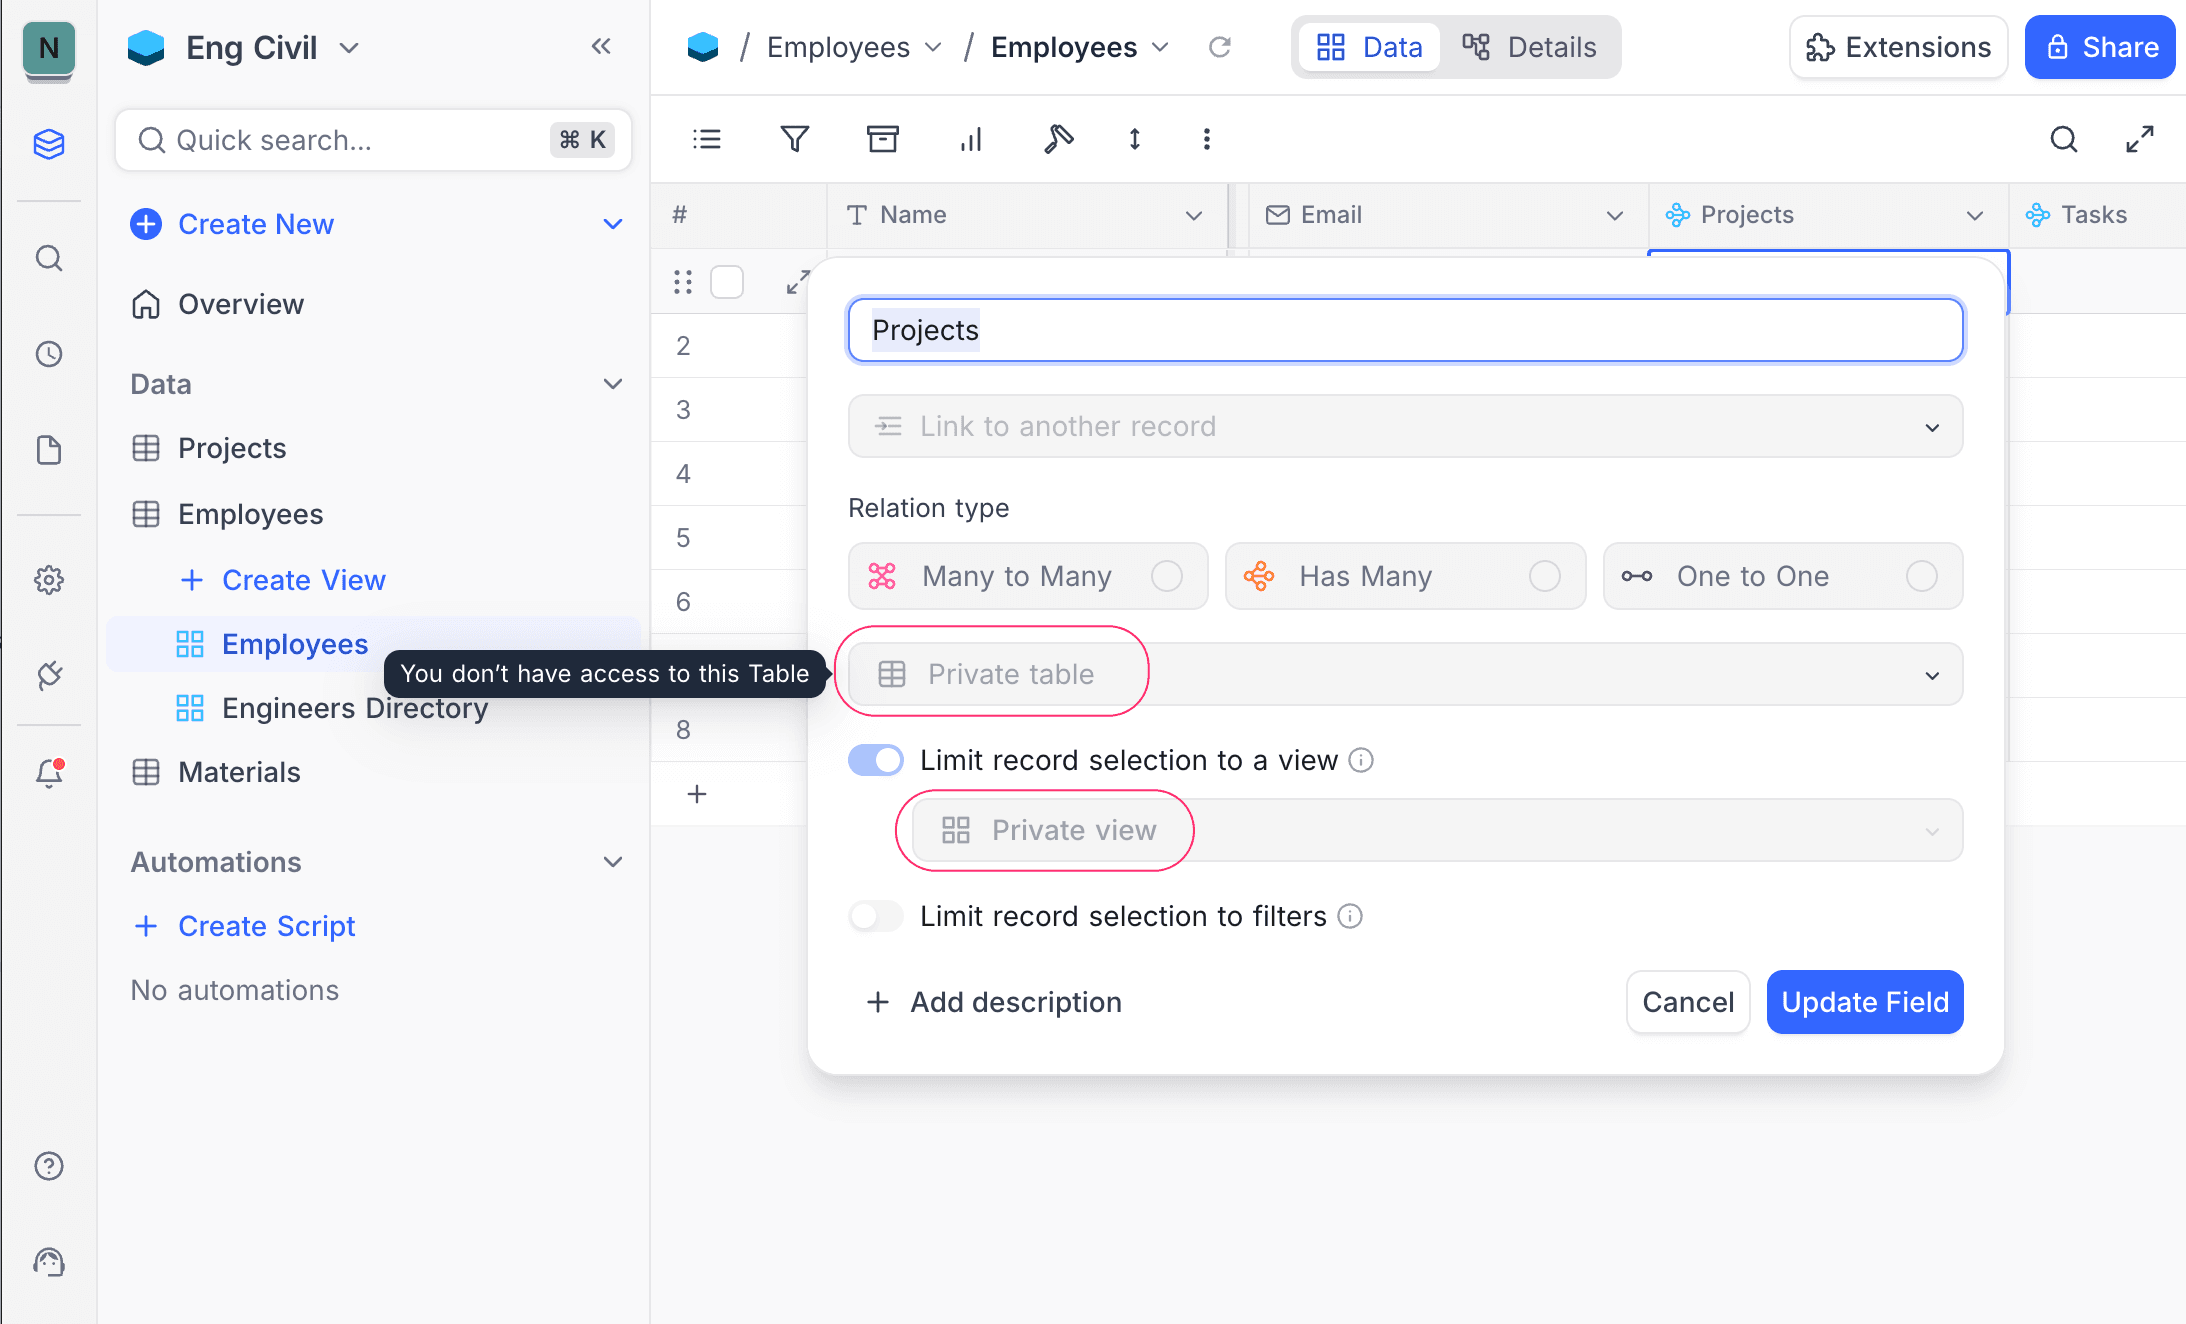
Relational fields When a table is hidden from a user, relational fields that link to that table show only the display values of the linked records. If the role of the user allows it (Editor+), the user can still link or unlink records from the source table. But the user cannot open or access the linked records. Lookup and Rollup fields that read through the hidden table are empty for that user.
For a relational field that links to a hidden table, the edit modal shows the table name as "Private Table" and the view name as "Private View".
Dashboards A widget that reads a table hidden from you shows Incomplete configuration instead of its data, the same as a widget whose table was deleted. You cannot point a new or an existing widget at a table that is hidden from you.
Duplicating projects When a user duplicates a project, NocoDB copies only the tables that this user can see. The new project does not include tables that are hidden from that user. Thus, the new project also does not include relational fields that link to hidden tables. Formula fields that refer to these relational fields can show errors because the references are missing.
Table Record Permissions
Table Record Permissions set the actions that a user can do on the records in a table. When you give permission, users can create or delete records as their roles and access levels allow. When you restrict permission, those actions are disabled. The table and its records can still be visible to the user.
Configuring Record Permissions
To set record permissions for a table:
- In the sidebar, click the
⋯icon next to the table name. - Select Edit table permissions.
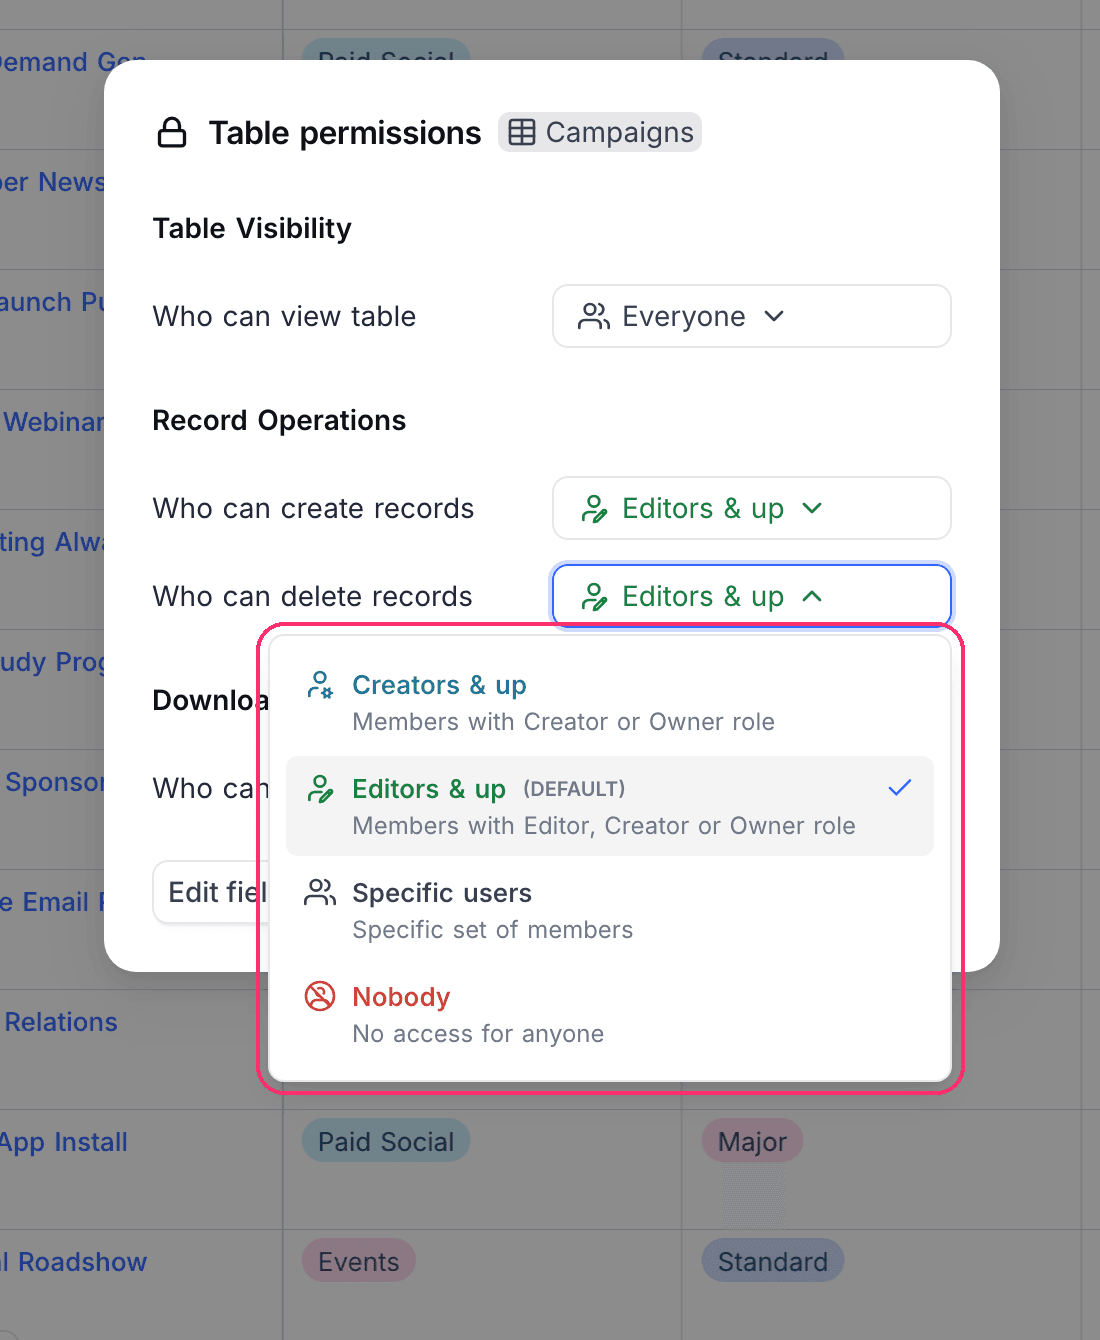
- Use the dropdown menus to set who can:
- Create records
- Delete records
Permission Levels
You can give a different access level to each action (create record or delete record). These are the options:
| Option | Who gets access |
|---|---|
| Editors & up | Members with Editor, Creator, or Owner roles (default) |
| Creators & up | Members with Creator or Owner roles |
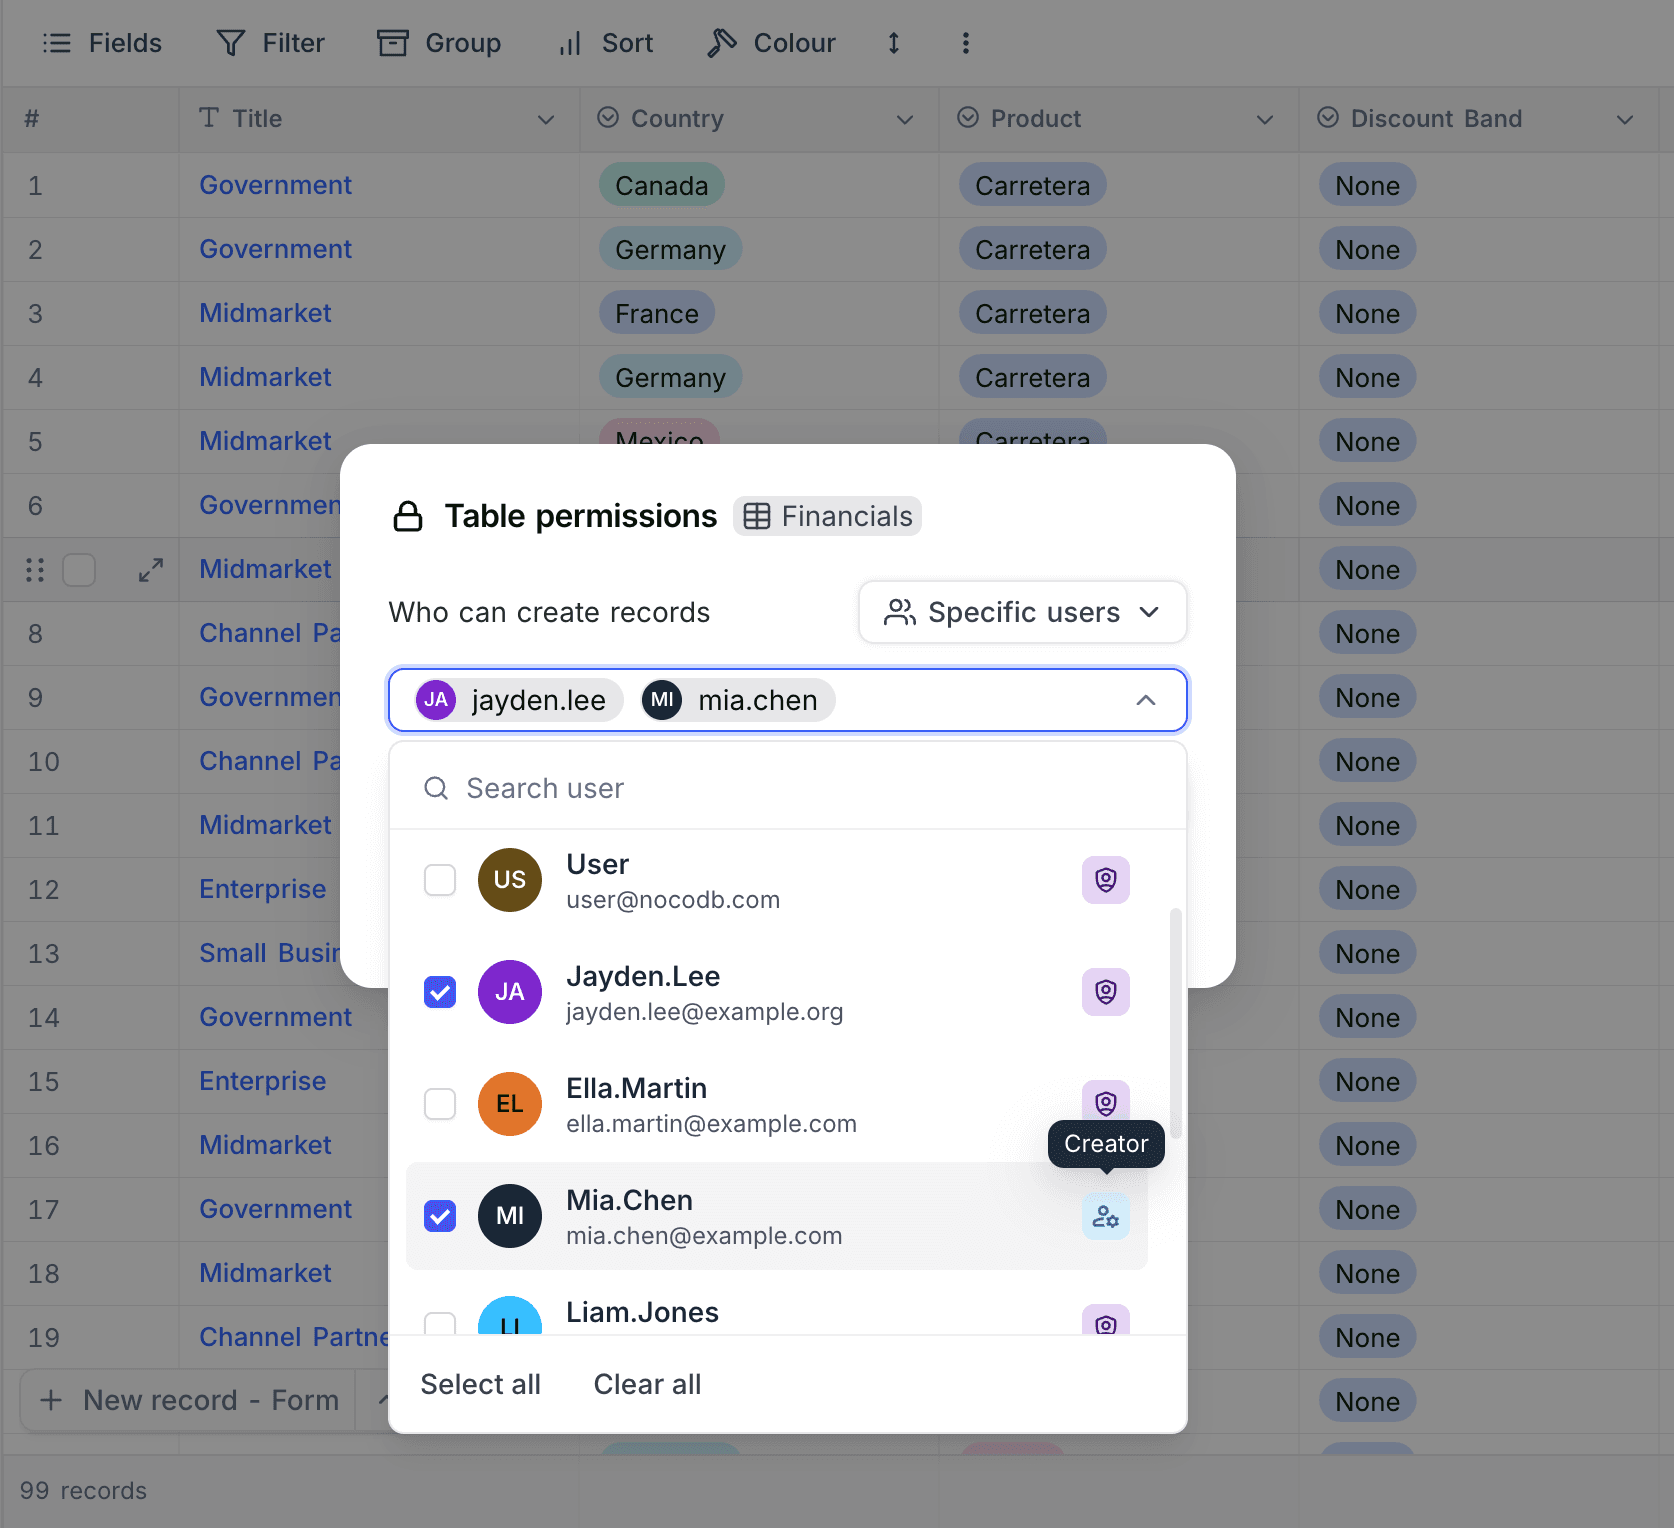
| Specific users | Selected members or teams |
| Nobody | No one can perform this action |
By default, members with the Editor role and higher can create and delete records in a table.
| To | Select |
|---|---|
| Let only creators and owners do the action | Creators & up |
| Stop all record creation or deletion | Nobody |
| Let only selected members or teams do the action | Specific users |
Record Permission Notes
- Table permissions do not control record visibility. Users with access can still see all records. Table permissions control only who can create or delete records.
- Permissions apply at the table level, to all records in the table. You cannot set them for one record or for a subset of records.
- Table permissions are independent of field permissions. You can set each one separately.
- Table permissions also apply to:
- Record creation or deletion through APIs
- Record creation through shared forms
Table Download Permission
The table download permission sets who can export the data of a table as CSV, Excel or JSON. By default, every member of the project can download the data of every table.
Members outside the permission do not see the Download menu in the toolbar or in the view context menu, and the table is not offered in the Data Exporter extension. NocoDB also refuses an export that these members request through the API or an MCP client. Reading records through the API is not affected.
Configuring the Download Permission
To set who can download the data of a table:
- In the sidebar, click the
⋯icon next to the table name. - Select Edit table permissions.
- Under Download Data, use the dropdown menu to set who can download.
- If you select Specific users, select the members or teams that can download.
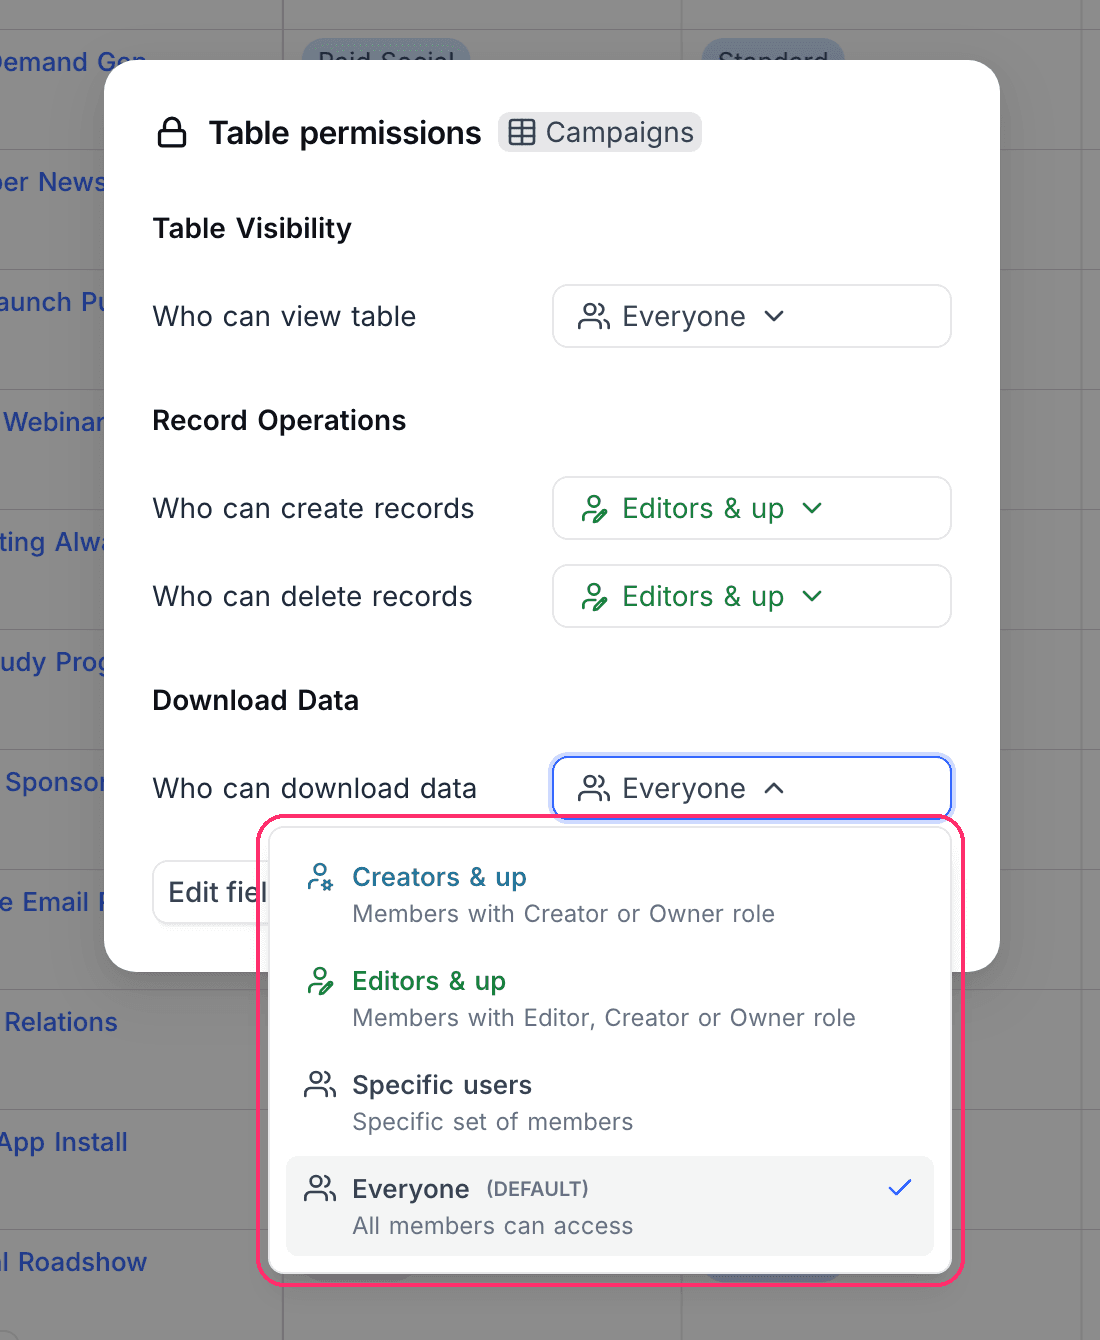
These are the options:
| Option | Who can download the data |
|---|---|
| Everyone | All members of the project (default) |
| Editors & up | Members with Editor, Creator, or Owner roles |
| Creators & up | Members with Creator or Owner roles |
| Specific users | Only selected members or teams |
Download Permission Notes
- A shared view keeps its own
Allow downloadtoggle. The table download permission does not change what a shared view link allows. - Resetting the table permissions gives the download back to everyone.
Permissions Overview
The permissions overview shows a summary of all table and field permissions in the project.
To open the permissions overview:
- Open Project Settings.
- Under Manage, click Data Permissions.
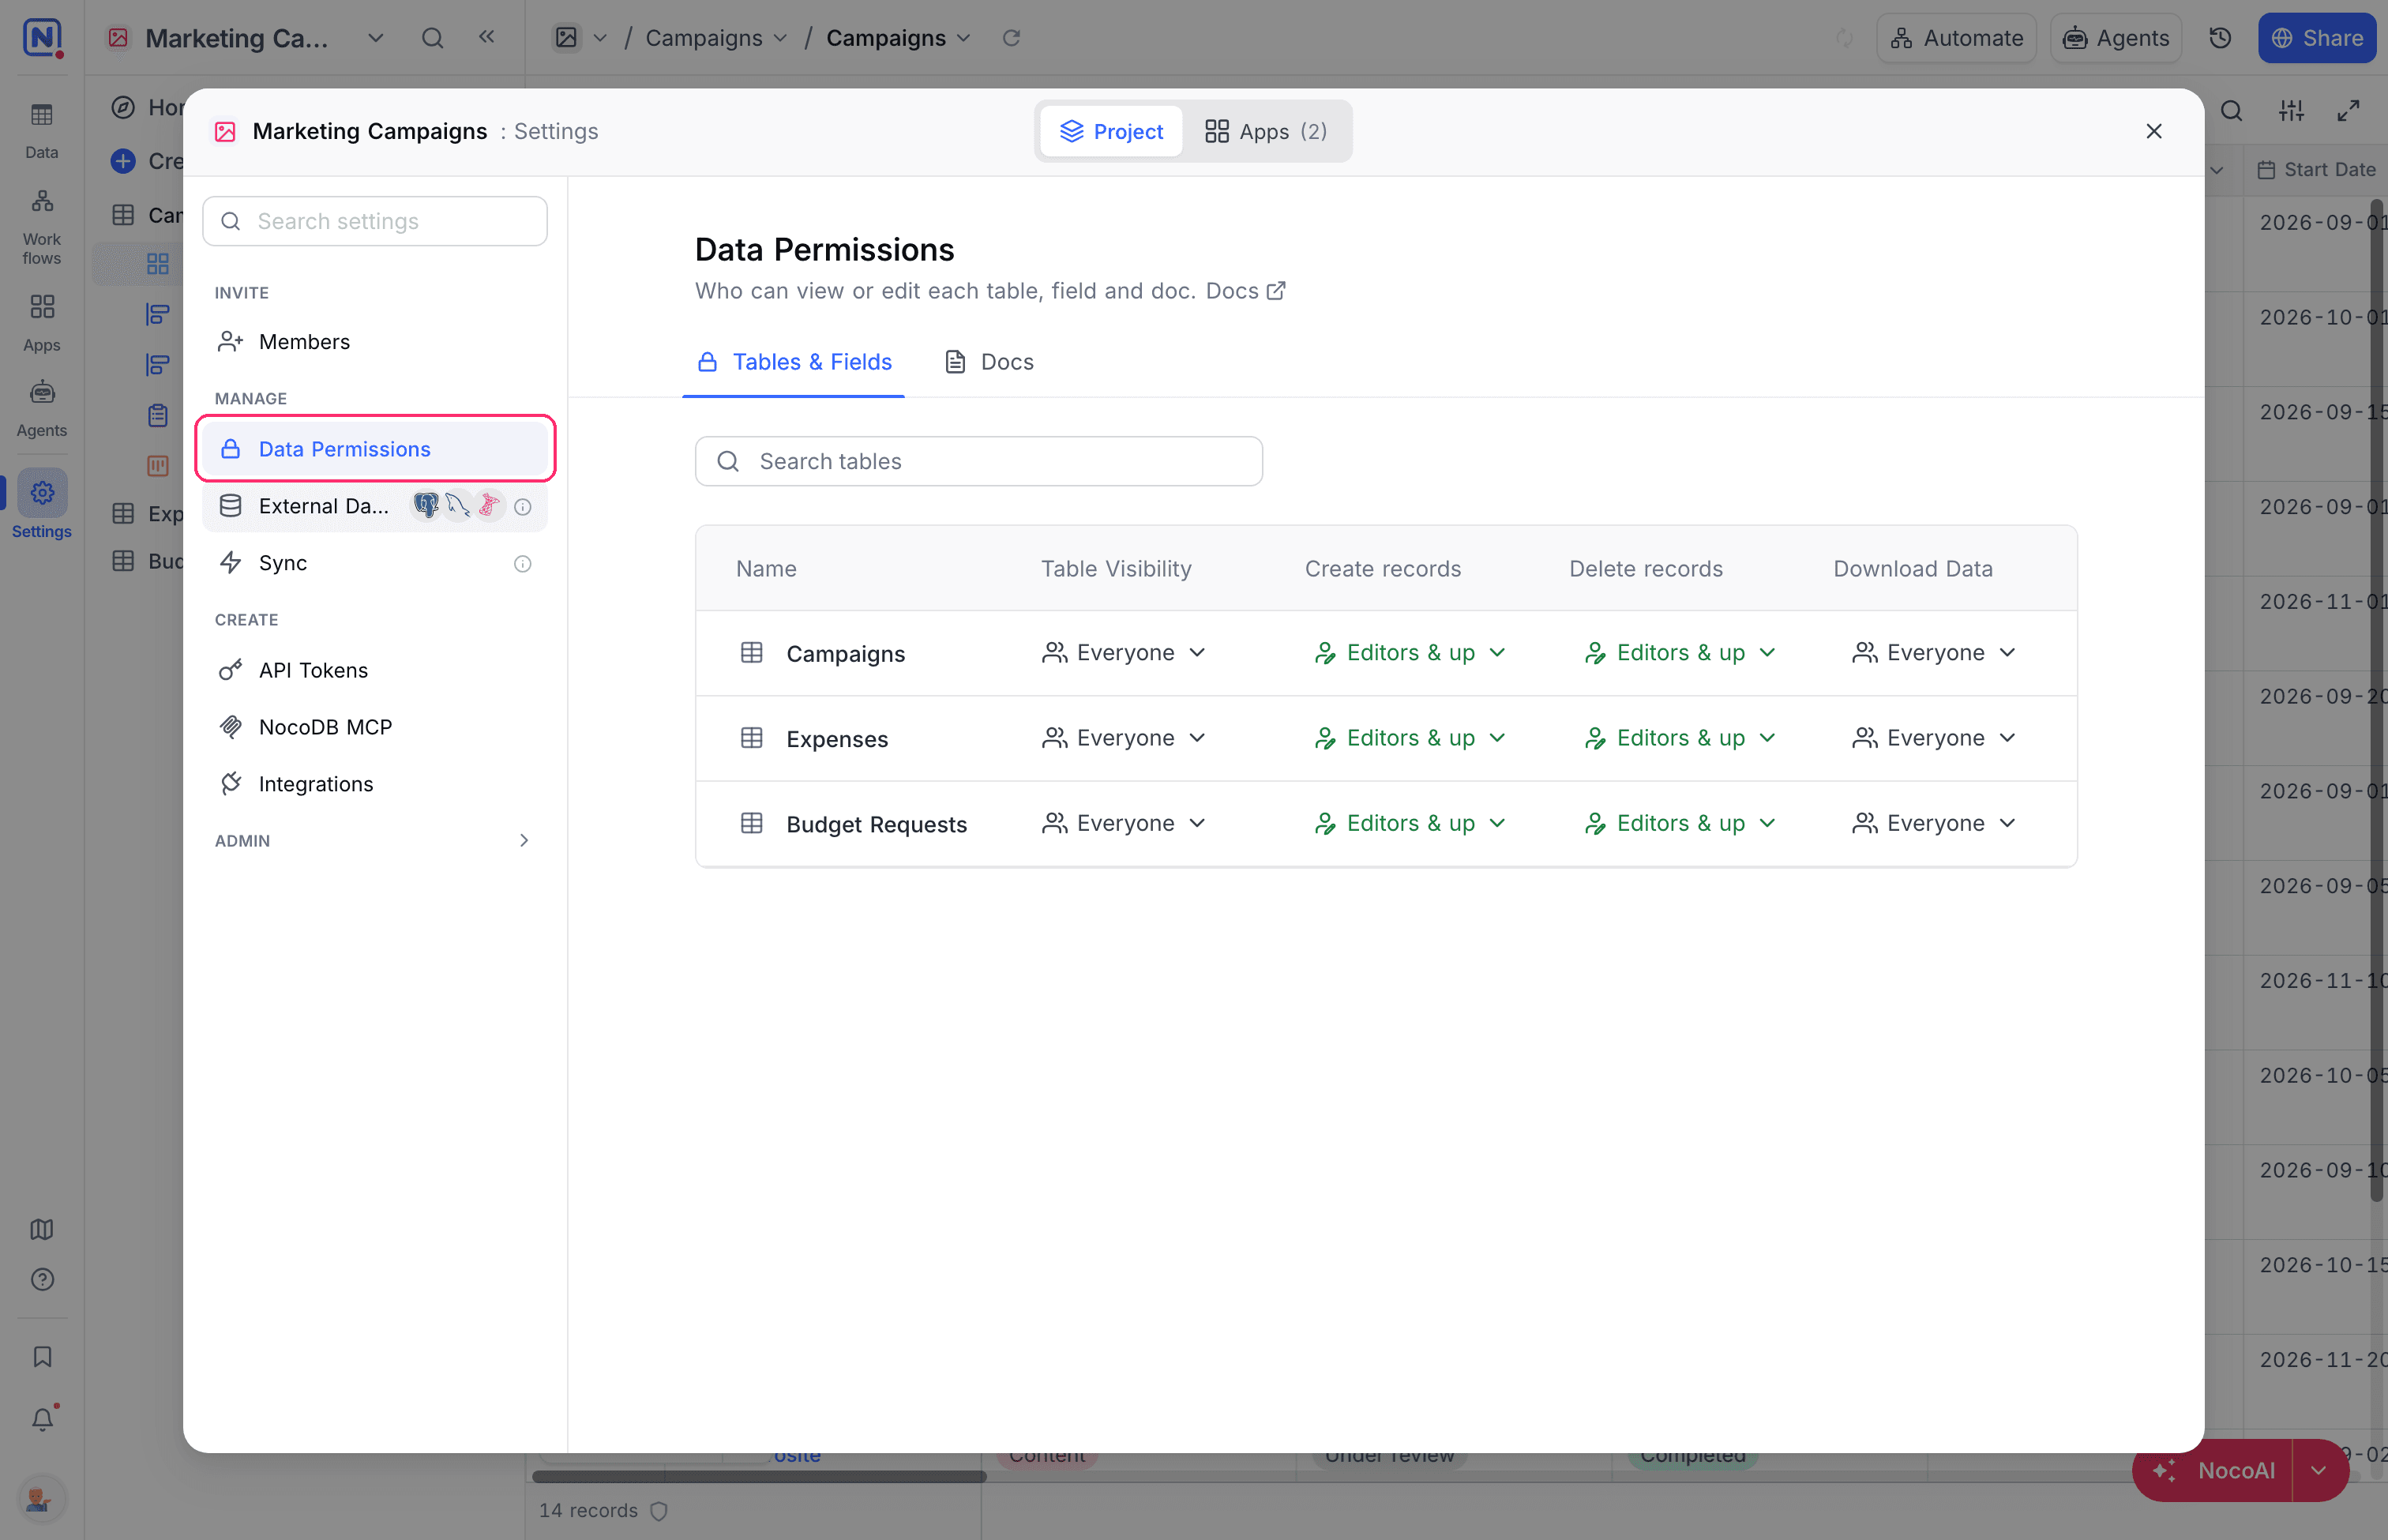
The Tables & Fields tab lists every table with who can see it, who can create records, who can delete records and who can download the data. You can change each permission from its dropdown menu.
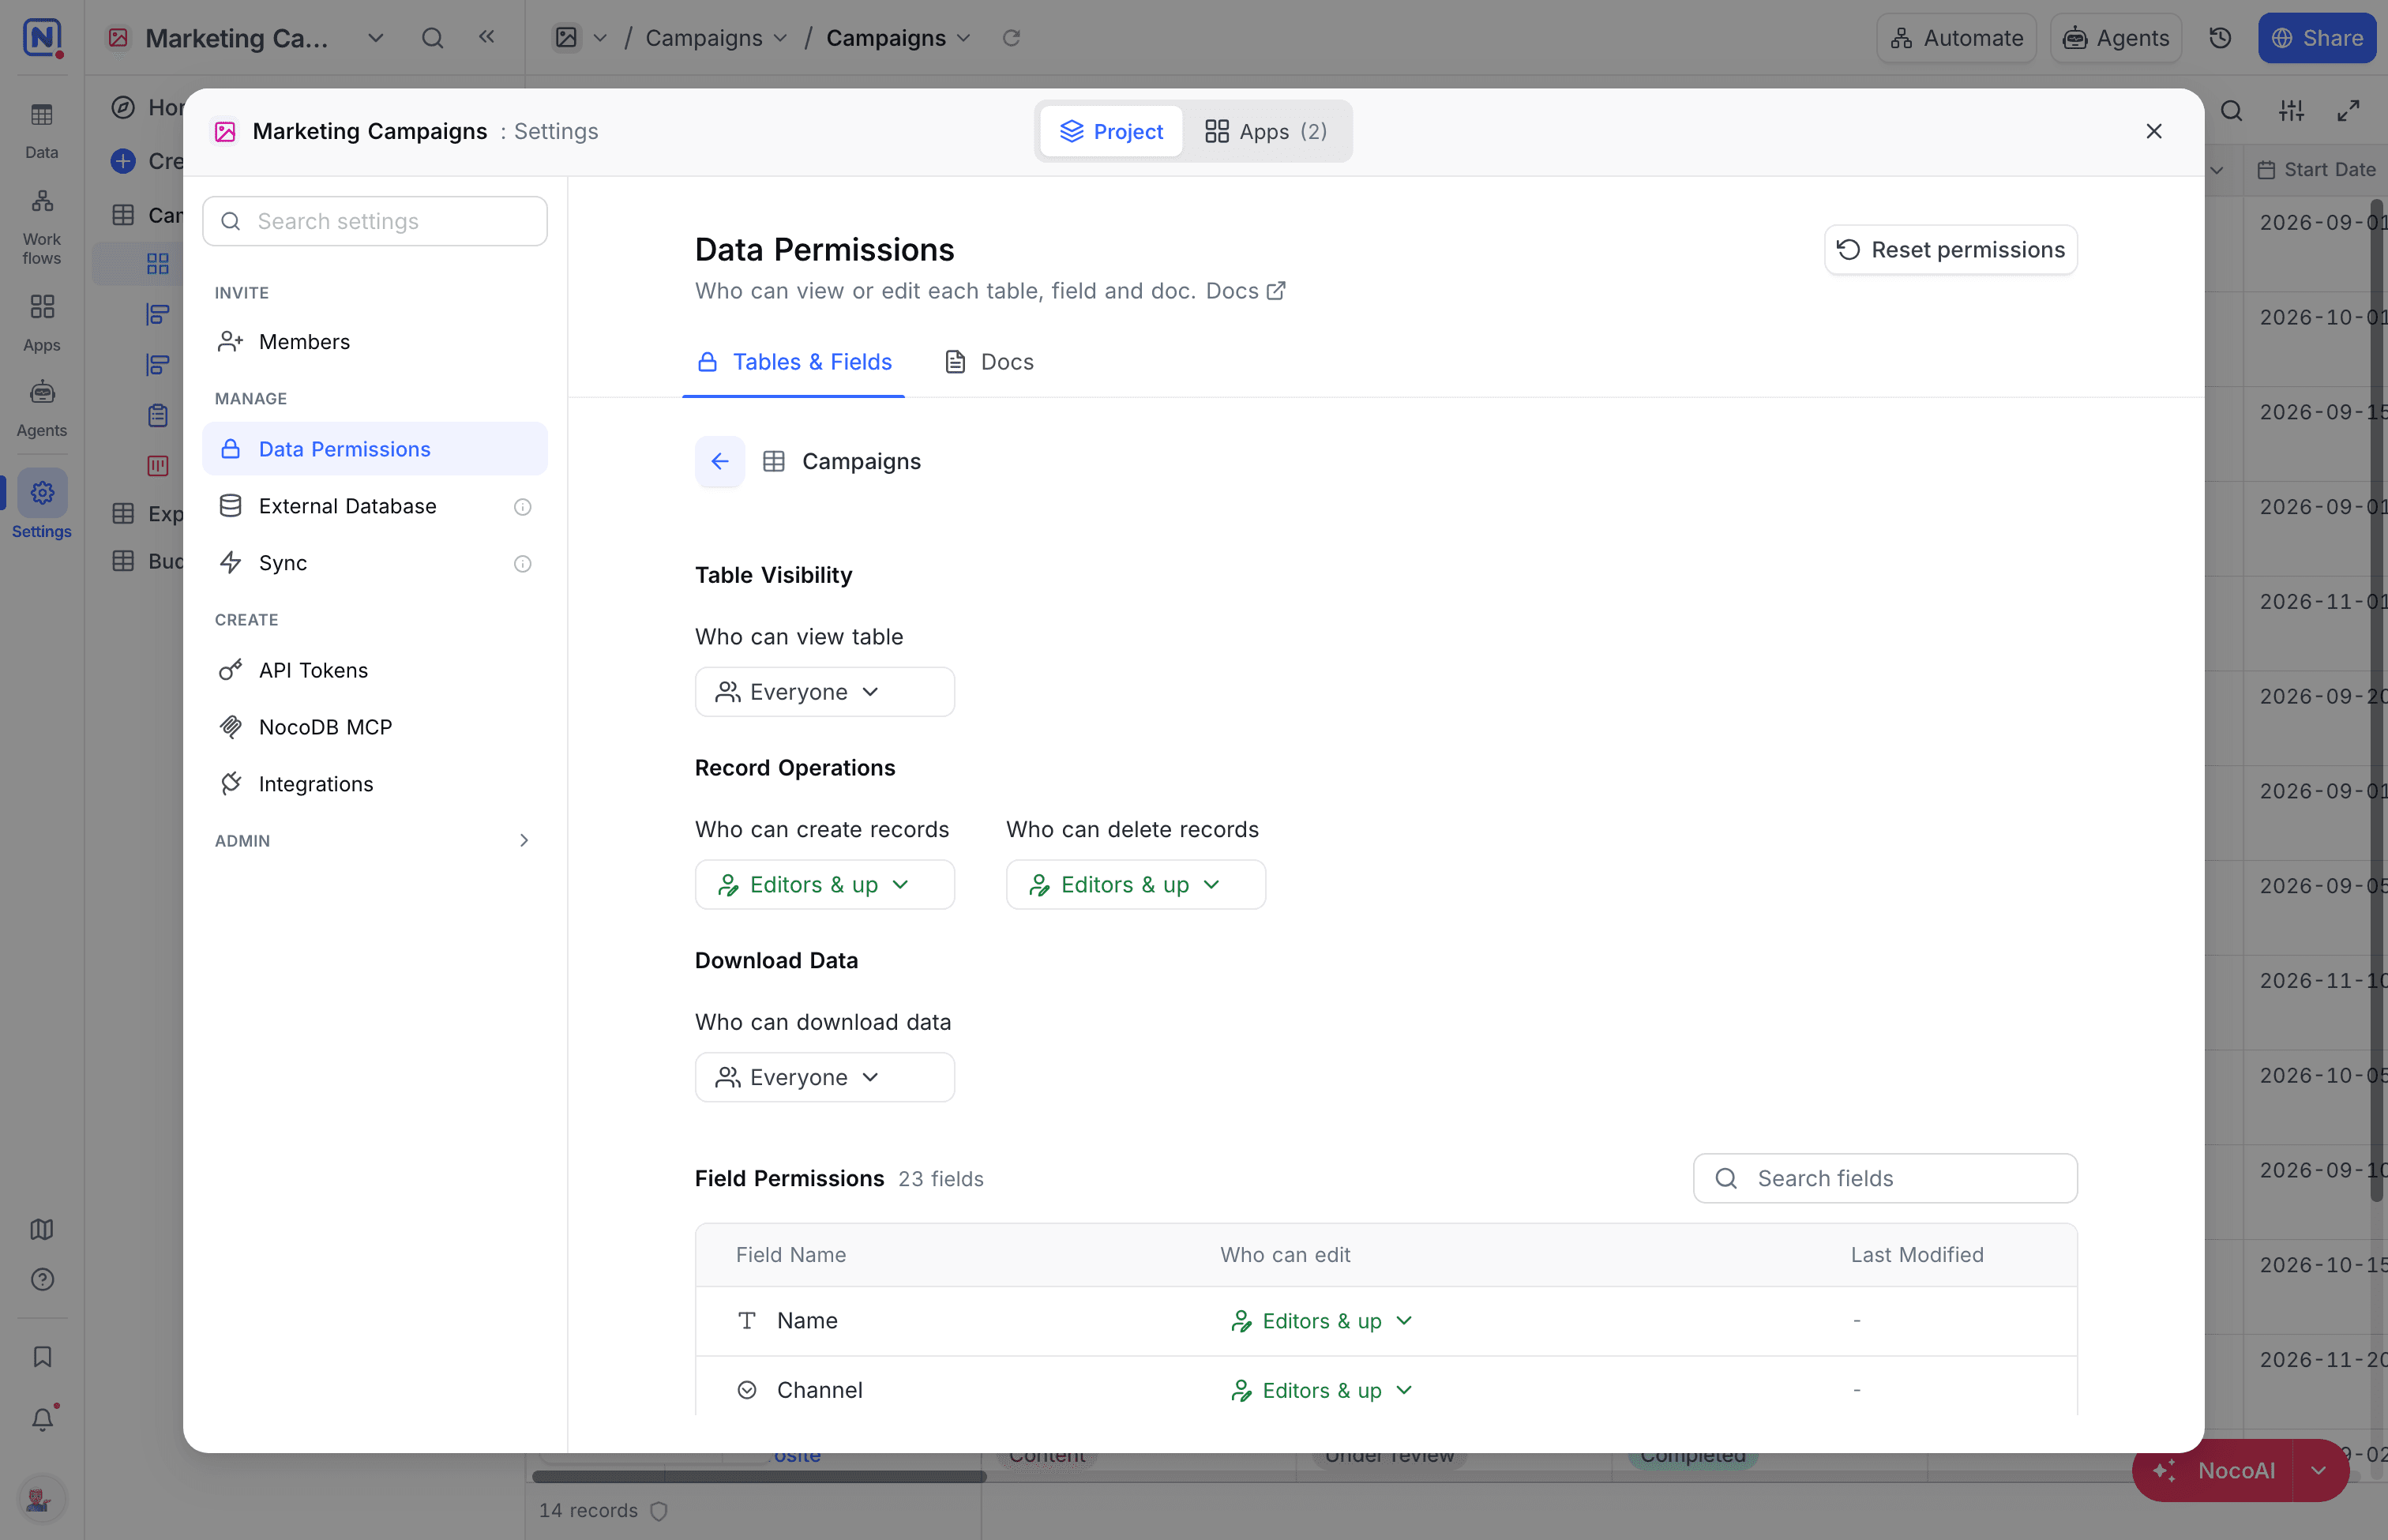
To see the field permissions of a table, click the table. The page shows its table permissions and, below them, who can edit each field.
Manage permissions with the API
The Meta API sets the same grants as the permission dialogs. GET /api/v3/meta/bases/{baseId}/permissions lists the grants of a project, PUT on the same path creates a grant or replaces the existing one for that table or field and permission, and DELETE /api/v3/meta/bases/{baseId}/permissions/{permissionId} removes one.
A grant names the table or field it is attached to, the permission (TABLE_VISIBILITY, TABLE_RECORD_ADD, TABLE_RECORD_DELETE, TABLE_DATA_DOWNLOAD or RECORD_FIELD_EDIT), and who gets it: a minimum role, a list of users and teams, or nobody.
Owners and creators can use these endpoints. Table visibility stays limited to owners, the same as in the dialogs.
For the request and response fields, refer to the Meta API reference.
Availability
- Table Record Permissions and the table download permission are available on NocoDB Cloud (Plus plan and above) and licensed self-hosted deployments (Business plan and above). Table Visibility is available on NocoDB Cloud (Business plan and above) and self-hosted Scale and Enterprise plans.
Last updated on